Full analysis is selected. Choose Quick brief to scan the key points first.
WFN QUICK BRIEF · UNDER 1 MIN
The short version
MODE 2 OF 2
The record
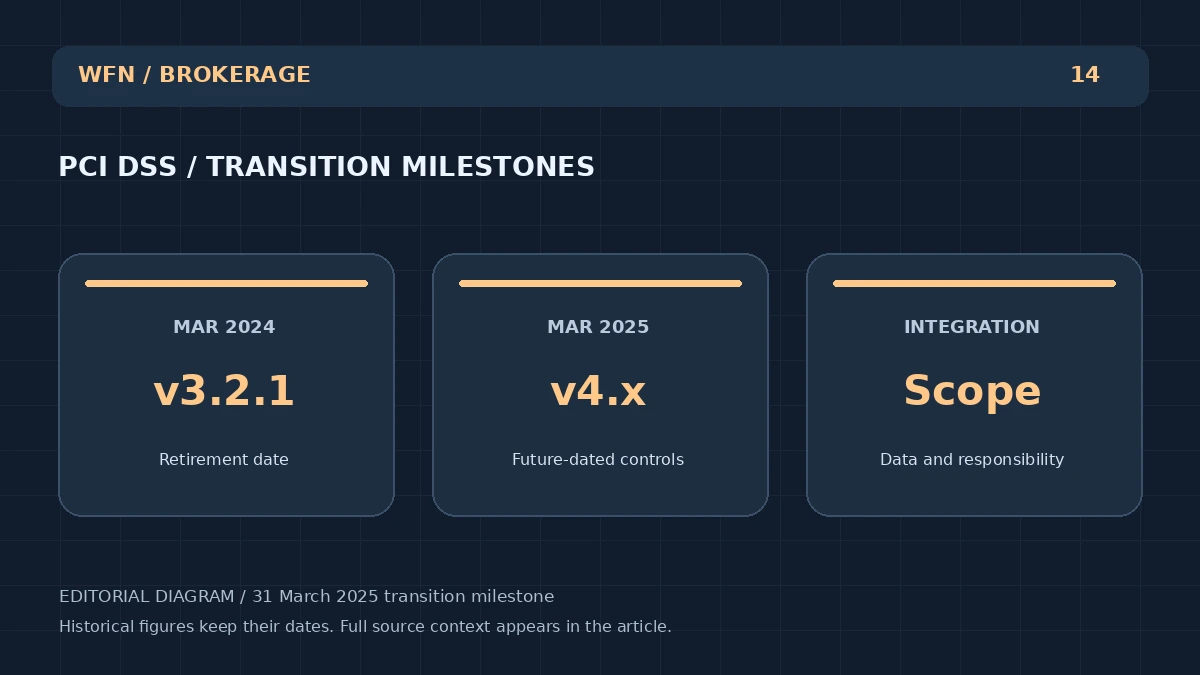
The PCI Security Standards Council’s transition guidance said PCI DSS v3.2.1 was retired on 31 March 2024 and that the future-dated v4.x requirements would take effect on 31 March 2025. The guidance presented this as a period for organisations to understand the requirements and implement necessary changes. PCI SSC guidance on future-dated v4.x requirements ↗
WFN analysis
For a brokerage integrating card payments, a functioning checkout is only one visible part of the service. The business needs to establish which parties and systems handle payment data and who owns the resulting security work.
Next check
Before making a current compliance claim, consult the applicable standard, assessment route and payment-provider requirements. Map data movement and responsibility through the chosen integration. Historical transition dates can explain why controls changed, but they cannot certify the security of today’s website or substitute for evidence from its actual payment environment.
Quick Brief is a reading aid. The full article and source trail stay on this page.
WFN STORY COMPASS
Choose your reading angle
Move between the reported record, market context and open questions. Status labels keep claims distinct from findings.
All context layers are visible. Choose a lens to jump to that part of the story.
MARKET CONTEXTWFN EDITION · 14 OCTOBER 2026
Editorial noteSource-based explanation with original WFN analysis. Historical records retain their dates. Original WFN editorial diagram; it is not a live market chart.
WFN REALITY LEDGER
What is on the record?
Primary-source analysis
Dated official record / historical or technical explainer
Primary record / reference period31 March 2025 transition milestone
The cited record establishes the documented event. Proposals, technical announcements, allegations and orders retain their stated status; WFN Analysis is editorial interpretation.
The PCI DSS v4.x transition illustrates why brokerage payment integration requires an identified security scope and ongoing ownership.
01 · VERIFIED RECORD
The verified record
The PCI Security Standards Council’s transition guidance said PCI DSS v3.2.1 was retired on 31 March 2024 and that the future-dated v4.x requirements would take effect on 31 March 2025. The guidance presented this as a period for organisations to understand the requirements and implement necessary changes. PCI SSC guidance on future-dated v4.x requirements ↗
The milestone concerns payment-data security requirements. It is not a brokerage licence, a merchant-account approval or a guarantee that a particular deposit will be accepted.
02 · WFN EDITORIAL ANALYSIS
Why it matters
For a brokerage integrating card payments, a functioning checkout is only one visible part of the service. The business needs to establish which parties and systems handle payment data and who owns the resulting security work.
Using an external provider can change that scope, but a claim about reduced scope must be supported by the actual integration. A redirect, an embedded page and a server-side handling flow should not be treated as equivalent simply because the customer sees the same deposit amount.
03 · WHAT TO CHECK NEXT
What to check next
Before making a current compliance claim, consult the applicable standard, assessment route and payment-provider requirements. Map data movement and responsibility through the chosen integration. Historical transition dates can explain why controls changed, but they cannot certify the security of today’s website or substitute for evidence from its actual payment environment.